A Minimum Viable System for Solo Founders: Website, Product, Payments, Data, and Automation
"Cloudflare's Pages limits document lists Free-plan build counts, build duration, file count, individual file size, and the rule that Pages Functions consume Workers quotas."
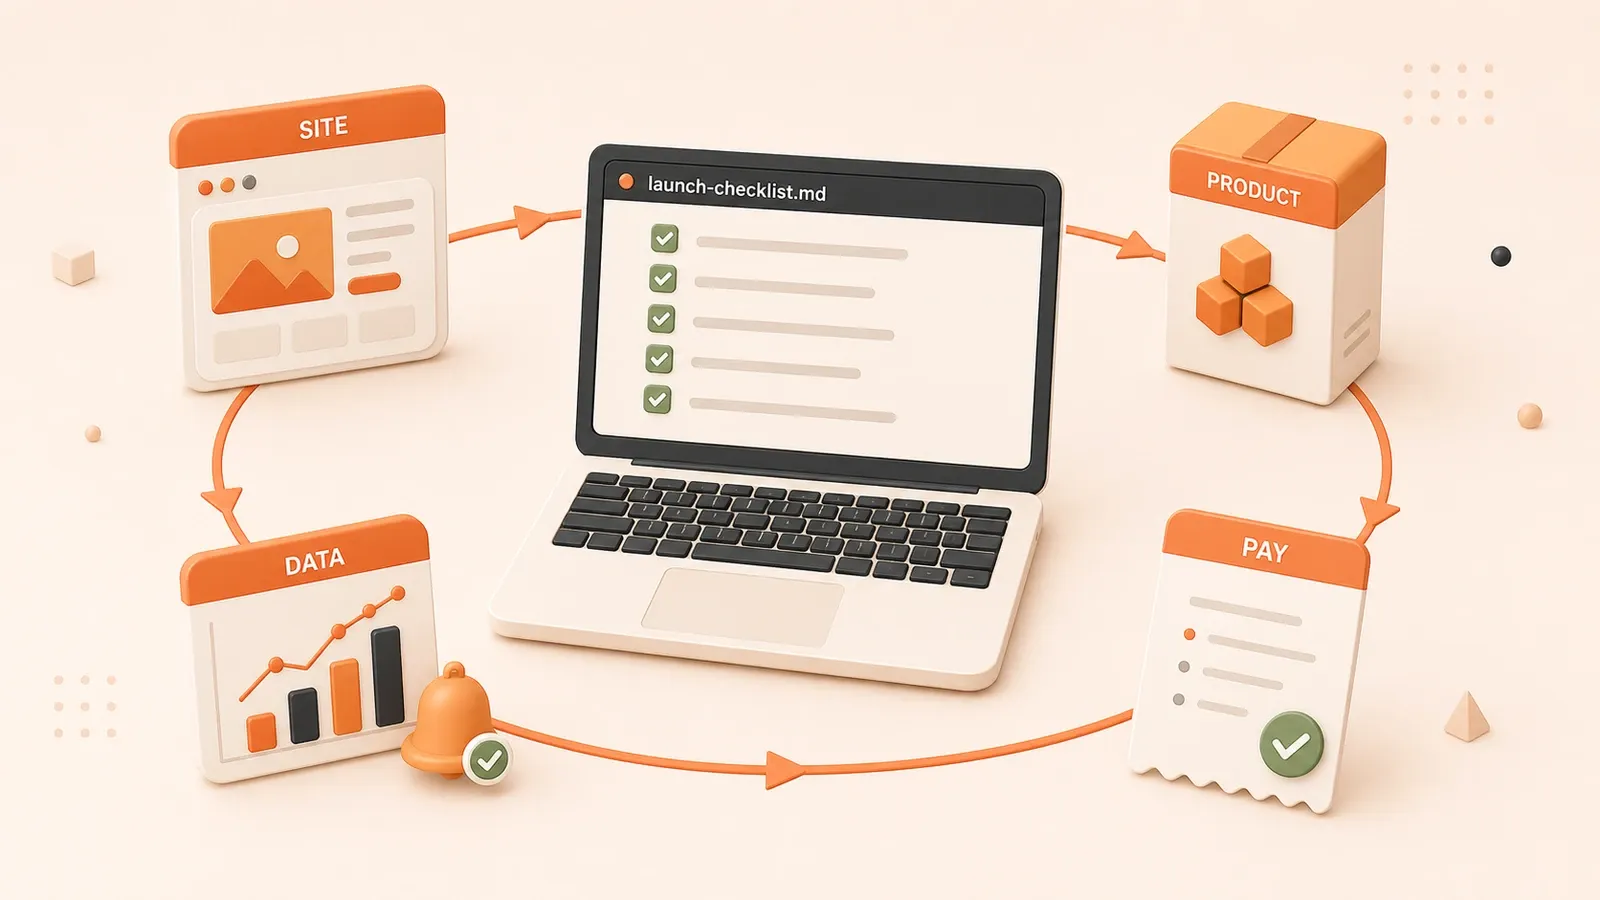
Open launch-checklist.md: the /pricing page exists, but the Stripe Product does not; login works, but subscription state never syncs; GA4 receives page_view, but a click on the payment button has no event; the feedback form sends email, but nothing enters a task queue.
Many indie developers treat “it runs” as the launch threshold. The gaps only become obvious when a paying customer still needs a manual email or a free allowance is exceeded before anyone has checked usage.
A minimum viable system for a solo founder is viable because its business actions complete, not because its tool list is short. A user can arrive, receive the product, pay, gain access, produce data, send feedback, and get help when something fails.
Use the first checklist to find the broken handoff. Then decide which layers need a minimal implementation and which can wait.
Minimum system checklist: interfaces that must close before launch
The acceptance standard is not “all features exist.” Each business action must run from trigger to result. Plenty of projects still add a Stripe webhook, Supabase RLS, and GA4 events on the night before launch because earlier work stopped at “the page renders.”
These are the interfaces worth testing before launch:
| Area | Interface that must close | Common omission | Acceptance action |
|---|---|---|---|
| Website entry | Pages load, routes avoid 404s, assets load, and build usage is monitored | Cloudflare Free build allowance is exceeded; nobody reads error logs | Visit the home and pricing pages on a real device; inspect Cloudflare Pages build history |
| Product form | The product has a clear form (content site/tool/SaaS), and pricing is visible | A product description exists, but there is no price or purchase path; the Stripe Product is missing | Check Products/Prices in Stripe Dashboard; visit /pricing and confirm the displayed offer |
| Complete payment flow | Checkout Session creation, webhook delivery, access activation, failure/cancel handling, and subscription sync all work | No webhook; payment succeeds but access is not granted; refund state never syncs | Complete a payment with a Stripe test method; inspect webhook logs and the subscription table |
| User system | Login works, RLS is enabled, subscription state syncs, and free and paid access differ | A login button exists, but RLS does not; every user can see paid content | Inspect the subscriptions table after login; use a free account to verify RLS |
| Data events | GA4/GSC are configured, 5–8 business events are tracked, payment/sign-up/trial are visible, and errors alert someone | GA4 only has page_view; payment clicks and completed sign-ups are absent | Verify collection in GA4 DebugView; inspect queries and pages in the GSC Performance report |
| Feedback loop | Feedback submits, enters a work queue, and support messages receive a response | The form only sends email, with no task board or follow-up state | Submit feedback and confirm that it enters the task board or mail queue |
| Automation boundary | Webhook/API/Cron work has usage thresholds, alerts, and rollback steps | A task fails silently; usage is noticed only after a limit is hit | Inspect Workers usage; configure a usage threshold and error monitoring |
| Cost monitoring | Cloudflare/Supabase usage is recorded, free limits are known, and an upgrade plan exists | An idle Supabase Free project is paused; Workers usage exceeds a limit unnoticed | Check Cloudflare usage and Supabase project activity; document upgrade triggers |
Each row requires a real action, not just a configuration review in the repository. Before launch, complete at least one full payment, one login and permission test, one event verification, and one feedback submission.
Website entry: the minimum deployment stack and its limits
The website is the first layer. A static site or light framework is a sensible starting point, but build counts, file counts, and dynamic functions still belong in the cost sheet. Cloudflare Pages and Astro reduce maintenance pressure; their free allowances are still limits, not architectural guarantees.
Stack selection table
| Product form | Suggested stack | Build cost | Dynamic function cost | Suitable use |
|---|---|---|---|---|
| Content site | Astro / Hugo / Hexo | Cloudflare Pages Free: 500 builds/month, 20,000 files, 25 MiB asset | Pages Functions count toward Workers | Blog, documentation, SEO pages, product pages |
| Tool site | Astro + API calls | Same as above | API calls count toward Workers (100,000 requests/day) | Single-page tools, lookup tools, calculators, data visualization |
| SaaS | Astro + Supabase | Same as above | Workers + Supabase Edge Functions | Multiple users, subscriptions, permissions, database reads and writes |
As of July 26, 2026, the official Cloudflare Pages limits still list 500 builds per month on Free, a 20-minute build timeout, up to 20,000 files, and a 25 MiB maximum asset. Pages Functions requests consume Workers quotas; Workers Free includes 100,000 requests per day and 10 ms of CPU per invocation.

Free static asset requests do not make the entire system free. A content product with many images, videos, or downloads must also account for object storage, CDN processing, transformations, and egress.
AI-generated pages still need user value
Google Search guidance for generative AI content permits AI-assisted research and organization, but generating many pages without added value may violate the scaled content abuse policy. A website entry point needs a real product, real feedback, and actual review, not hundreds of automatically produced SEO pages.
For content-site performance, see the Astro 5 performance guide. A minimum system does not need a Lighthouse 100 score before launch. It does need working pages, assets, CTAs, and visible build failures.
Product layer: content site, tool, or SaaS for the first version?
The product form determines the complexity of payments, users, data, and automation. Content sites, tools, and SaaS represent increasing operational commitments rather than three equivalent buttons. The first release should favor the form you know best, with the simplest payment and the least user data.
Product-form decision table
| Product form | Stack complexity | Payment complexity | User-data requirement | Fit for a first release |
|---|---|---|---|---|
| Content site | Low: static + CMS + SEO | Low: one-time payment or free | Low: email subscription, RSS, comments | High: useful for SEO acquisition, content monetization, and demand testing |
| Tool site | Medium: static + API + light backend | Medium: one-time payment or subscription | Medium: light user system and usage history | Medium: useful for validating a feature and charging once or repeatedly |
| SaaS | High: authentication + database + subscription + RLS | High: subscriptions, usage billing, refunds | High: multiple users, permissions, subscription state, data isolation | Low: best when paying demand is already clear and the stack is familiar |
Decision criteria
Choose the first form with three factors:
- Stack familiarity: if Astro or Hugo is familiar, a content site can validate demand quickly. A tool or SaaS carries less implementation risk when Supabase or Postgres is already familiar.
- Payment complexity: a one-time payment is usually simpler than a subscription, and a subscription is simpler than usage billing. Start with one-time payment or free lead capture and add complex billing when demand proves it necessary.
- User-data needs: a content site may only need email and RSS; a tool may need usage history; SaaS needs identity, permissions, subscription state, and data isolation.
Product form is not an identity. If one core action is still unreliable, an account center, team workspace, and template marketplace should not come first.
Payment layer: not a final button, but an input to the data model
Payments are the highest-risk layer in a minimum system. They influence the database, users, entitlements, admin tools, and notification design. If Checkout can charge but the webhook does not grant access, refunds do not update state, or expired subscriptions retain permissions, the result is a fulfillment failure.
Payment-flow checklist
A minimum Stripe payment loop includes these steps:
| Step | Stripe object | Interface that must close | Common omission |
|---|---|---|---|
| 1. Create a product | Products | Create a product in Stripe Dashboard and show its price on the pricing page | /pricing has a price, but no Stripe Product exists |
| 2. Create a price | Prices | Configure amount, currency, billing period, and one-time/subscription/usage model | A subscription has no interval; usage billing has no meter |
| 3. Create a Checkout Session | Checkout Session | Configure line_items, mode, success_url, and cancel_url | success_url redirects without verifying payment state |
| 4. Configure a webhook | Webhook endpoint | Receive events such as checkout.session.completed, invoice.paid, and customer.subscription.deleted | No webhook; successful payment never grants access |
| 5. Fulfill the order | Custom logic | Grant access in the database and send confirmation after payment | Access depends on an untracked manual action |
| 6. Handle refunds | Refunds | Update state, revoke access, and notify the user after a refund | A refunded user still has paid access |
| 7. Sync subscription state | Subscriptions | Update state after renewal, cancellation, or expiration | Access remains after the subscription expires |
Payment-model decision table
The billing model changes the data model:
| Payment model | Data-model effect | Access management | Suitable use |
|---|---|---|---|
| One-time payment | Add paid_at or purchase_id to the user or purchase record | Grant access once, permanently or for a fixed period | Digital products, courses, templates, single-purchase tools |
| Subscription | Create a subscriptions table with user_id, stripe_subscription_id, status, and current_period_end | Grant and revoke access by period; state must sync | Tools, SaaS, membership content |
| Usage billing | Create a usage table with user_id, meter, amount, and timestamp | Enforce usage and balances; requires an allowance table | APIs, cloud storage, compute services |
Stripe Products and Prices let you create a new Price and transfer a lookup key to it. Looking up prices by key can avoid hard-coding a Price ID in multiple places, but changing prices still requires the official create-and-activate workflow.
Fulfillment, refunds, and subscription state need webhook and database logic. A frontend success page or manual Dashboard check is not enough. For a deeper payment-platform and data-model comparison, continue with the solo-founder payment systems guide.
Test-payment verification
Before launch, complete an end-to-end payment in the Stripe test environment:
- Use the Stripe Dashboard test environment
- Use the current Stripe-documented methods for successful, failed, and additional-authentication payments
- Complete Checkout with the test details
- Inspect Payments and Events and confirm that the expected event fired
- Inspect the
subscriptionsor entitlement record and confirm that state synced - Log in to verify granted access, then repeat with an account that has no entitlement
After test validation, verify production keys, the webhook endpoint, event signatures, and notifications separately.
User layer: distinguish identity, permissions, and subscription state
A user system is more than a login button. The minimum version must distinguish identity, permissions, subscription state, and data-access boundaries. If login succeeds but every user can read paid data, the problem is authorization rather than the login component.
Supabase Auth can handle password, magic link, OTP, social login, and SSO. JWTs and database RLS work together on authorization. Authentication answers “who are you”; an RLS policy decides which rows you may read or write.
Minimum user-system checklist
| User capability | Supabase capability | Interface that must close | Common omission |
|---|---|---|---|
| Authentication | Password, magic link, OTP, social login, SSO | The user can sign in, receive a JWT, and access their own data | A login button exists, but authorization is absent |
| Permission management | RLS (row-level security) | Users only access their own data; paid users access paid content | RLS is disabled or a policy is too broad |
| Subscription sync | Stripe webhook → subscriptions table | State updates after payment, renewal, cancellation, or expiration | State remains in Stripe and never reaches the application |
| Data boundary | RLS policy | Users access their own rows; administrator paths use separate privileges | No isolation test; one user can see another user’s data |
A Supabase project uses Postgres as its data foundation, with Auth, Storage, Realtime, and Edge Functions working around that project. Subscription state should be updated by a trusted backend; the browser must not decide whether a user owns paid access.
Before launch, verify RLS with at least two accounts, one entitled and one not. Also confirm that no service-role or other high-privilege key is exposed to the browser.
Data layer: 5–8 business events, not just an analytics script
Installing GA4 is not a data layer. The minimum version only needs 5–8 business events that can change a decision, but they should cover visits, clicks, core actions, sign-up, payments, errors, and feedback.
Business-event checklist
| Business event | GA4 event name | Trigger | Review purpose |
|---|---|---|---|
| Page view | page_view | Page load | Entry-page and SEO acquisition analysis |
| Payment-button click | begin_checkout or a custom event | User clicks purchase or subscribe | Conversion funnel and pricing-page performance |
| Completed sign-up | sign_up | User completes registration | Registration conversion and acquisition quality |
| Trial start | Custom trial_start event | User begins a trial or free experience | Trial conversion and experience improvement |
| Completed payment | purchase | Backend confirms successful payment | Revenue analysis and payment-flow improvement |
| Error or crash | Custom error_occurred event | Frontend error, API failure, or core-action exception | Reliability and error prioritization |
| Submitted feedback | Custom feedback_submit event | User sends feedback or a problem | Feedback rate and issue classification |
GA4 can mark business-critical actions as key events. Realtime and DebugView verify collection, while production review also needs correct parameters, attribution, and deduplication.
Data-review routine
Review the system at least weekly:
- GA4: inspect business events: verify collection in DebugView, then review the path from visit to sign-up, trial, and payment.
- GSC: inspect queries and pages: review clicks, impressions, CTR, average position, queries, and pages rather than total traffic alone.
- Product analytics: decide when detail is needed: add PostHog or a similar tool when GA4 aggregation cannot explain what a specific user did, how often, or where a flow lost them.
GSC, logs, and error alerts matter before revenue. They expose acquisition queries, pricing friction, failed core actions, and common errors. If collection begins only after the first paying customer, earlier failure causes are usually gone.
Automation layer: what belongs on day one and what adds risk
Some automation removes safe repetition; other automation magnifies damage when it fails. AI coding tools can speed up development, but they cannot validate payment fulfillment, permissions, security, or business data.
Coding agents such as Codex can help understand a repository, implement features, review changes, debug, test, and migrate code. They are development collaborators. Payment fulfillment, access boundaries, production secrets, usage alerts, and user feedback still need an accountable reviewer.

Automation-boundary table
| Automation | Worth doing on day one | Added risk | Usage threshold |
|---|---|---|---|
| Deployment automation | Build and deploy after Git push | Build allowance is exceeded; failures notify nobody | Pages build count and timeout |
| Notification automation | Payment event → entitlement record → confirmation | A webhook fails without retry; notification and access state disagree | Workers requests, CPU, and retry volume |
| Backup automation | Export critical data; enable platform backups on a paid plan | Free plans do not include automatic backups; failed exports go unnoticed | Database size, storage, and restore verification |
| Review automation | Export GA4/GSC data and generate a periodic report | Frequency is excessive; API quotas and data delay are ignored | GA4/GSC API quota |
| Complex orchestration | Observable payment → access → email → CRM workflow | One failure breaks the chain; no idempotency or rollback exists | Per-step failure, retries, and dead letters |
| Cross-system dependencies | Webhook, API, Cron, email, and CRM integration | Systems have different delays; failures lack unified logs | Dynamic requests, queues, and external API quotas |
Thresholds for Webhook, API, and Cron work
Webhooks, light APIs, and Cron jobs can run on Cloudflare Workers, but current platform limits belong in the cost sheet:
- Workers Free: 100,000 requests/day and 10 ms CPU/invocation.
- Workers Paid: starts at $5 per account per month; Standard includes 10M requests/month and 30M CPU ms/month, with usage pricing beyond the included amounts.
Static asset requests and dynamic Worker requests follow different billing rules. Monitor the combined cost of requests, CPU, retries, logs, KV, Queues, R2, and related products instead of watching one “free request” number.
Deployment notifications, payment confirmation, feedback routing, and periodic summaries are good early automation. Automatic refunds, production-data deletion, permission changes, bulk messages, and price changes should keep a human approval step until auditing, idempotency, and rollback are proven.
Cost thresholds: a free allowance is not an architecture promise
A free allowance is a startup budget, not an architecture promise. Cloudflare and Supabase limits depend on dynamic requests, CPU, storage, egress, builds, logs, and usage patterns. They cannot guarantee “free forever” or a fixed user count.
Cost and boundary table
| Service | Free allowance | Paid starting point or upgrade path | Change risk | Boundary to monitor |
|---|---|---|---|---|
| Cloudflare Pages | 500 builds/month, 20,000 files, 25 MiB asset, 20-minute build timeout | Upgrade Pages limits through the relevant Cloudflare account plan | Quotas and plan boundaries may change | Build count, file count, build timeout |
| Cloudflare Workers | 100,000 requests/day, 10 ms CPU/invocation; static asset requests are free | Paid starts at $5/account/month and includes 10M requests and 30M CPU ms | Price, CPU, requests, and related-product quotas can change | Request count, CPU, retries, and usage alerts |
| Supabase | 50,000 MAU, 500 MB database, 1 GB storage, 5 GB egress, 2 Free projects; idle projects may pause after one week | Pro is $25/month and includes $10 in compute credits | Project, compute, traffic, and security limits can change | MAU, database, storage, egress, project activity |
These figures were checked on July 26, 2026 against Cloudflare Pages limits, Workers pricing, and Supabase pricing. Check the official pages again at launch because quotas and billing models change.
An idle Supabase Free project may pause after one week, and the Free plan does not include automatic backups. Do not treat “the project still opens” as a health check. Verify activity, exports, restoration, and upgrade triggers.
For more Cloudflare boundaries, continue with the Cloudflare Free limits checklist and the Cloudflare plan comparison.
Summary
A solo founder’s minimum viable system is not the shortest tool list. Every important business action needs an entry point, an outcome, and a failure path: users can arrive, receive the product, pay, gain access, produce usable data, send feedback, and get help when something breaks.
The first release does not need to be perfect, but it must be testable. Keep launch-checklist.md beside the repository and run the payment, permission, event, feedback, and incident drills through a real user path. Frontend, backend, deployment, databases, payments, and analytics can grow later without forcing a full rebuild around a missing handoff.
Validate the first chargeable system for a solo business
Follow a real user path and verify the entry point, product action, payment fulfillment, user access, data, feedback, and incident handoff.
⏱️ Estimated time: 60 min
- 1
Step 1: Map one real business path
Start with a landing page or content page, then write down the CTA, core product action, payment or lead capture, access activation, and feedback entry. - 2
Step 2: Complete one core delivery
Run a real input through processing, success, failure, and retry states, and confirm that each core action leaves a traceable record. - 3
Step 3: Verify payment and access
Complete successful, failed, and additional-authentication payments in a test environment, then check the webhook, order, subscription status, and permissions. - 4
Step 4: Check the minimum event set
Verify visits, CTA clicks, core actions, sign-up, payment, feedback, and error events, and confirm that GA4, GSC, or product analytics can answer the important questions. - 5
Step 5: Submit feedback and trigger human follow-up
Send feedback from the product, confirm that it reaches one task queue, and retain its source, user, page, time, and handling status. - 6
Step 6: Set cost and incident thresholds
Record limits for dynamic requests, CPU, database size, storage, egress, builds, and pausing, then define notification, manual verification, and rollback actions.
FAQ
Does the first version of a solo-founder product need login?
Should the minimum version start as a content site, a tool, or SaaS?
What should an indie developer design before adding payments?
Is GA4 enough, and when should I add PostHog?
Why add GSC, logs, and error alerts before the product earns money?
Can free Cloudflare and Supabase allowances support an early product?
Can an AI coding tool build the entire system at once?
15 min read · Published on: Sep 24, 2026

Solo Founder Tech Stack Guide: Build, Automate, Ship, and Grow
If you landed here from search, the fastest way to build context is to jump to the previous or next post in this same series.
Previous
Choosing a Solo Founder Tech Stack: Content Sites, Tools, and SaaS
Map a maintainable solo-founder stack across content, validation, SaaS, payments, automation, data, and operations, with clear timing and cost boundaries.
Part 1 of 5
Next
Content Site, Tool Site, SaaS: A Three-Layer Product Stack for Solo Founders
Use search demand, tool actions, repeat usage, and payment signals to decide whether to improve content, build a free tool, sell a digital product, or build SaaS.
Part 3 of 5


Comments
Sign in with GitHub to leave a comment